Mayumiotero – Android security threats continue to evolve, but RatHat adds a notable element to the equation. Researchers at Zimperium’s zLabs disclosed the malware on September 16, 2026. According to their analysis, RatHat combines established Android attack techniques with generative AI. It targets sensitive information while attempting to gain deeper control over an infected device. The malware can pursue banking credentials, authentication codes, and other valuable data. However, its significance goes beyond information theft. RatHat also abuses legitimate Android features to expand its access after installation. Therefore, the threat illustrates how familiar attack methods can become more adaptable when AI enters the workflow. For everyday Android users, the lesson is straightforward. A convincing app icon or familiar name does not guarantee that an application is safe.
Read Also: AI-Tuned RTX 5090 Laptop Breaks Power Limit and Delivers Huge Performance Gains
Deceptive Apps Can Open the Door to RatHat
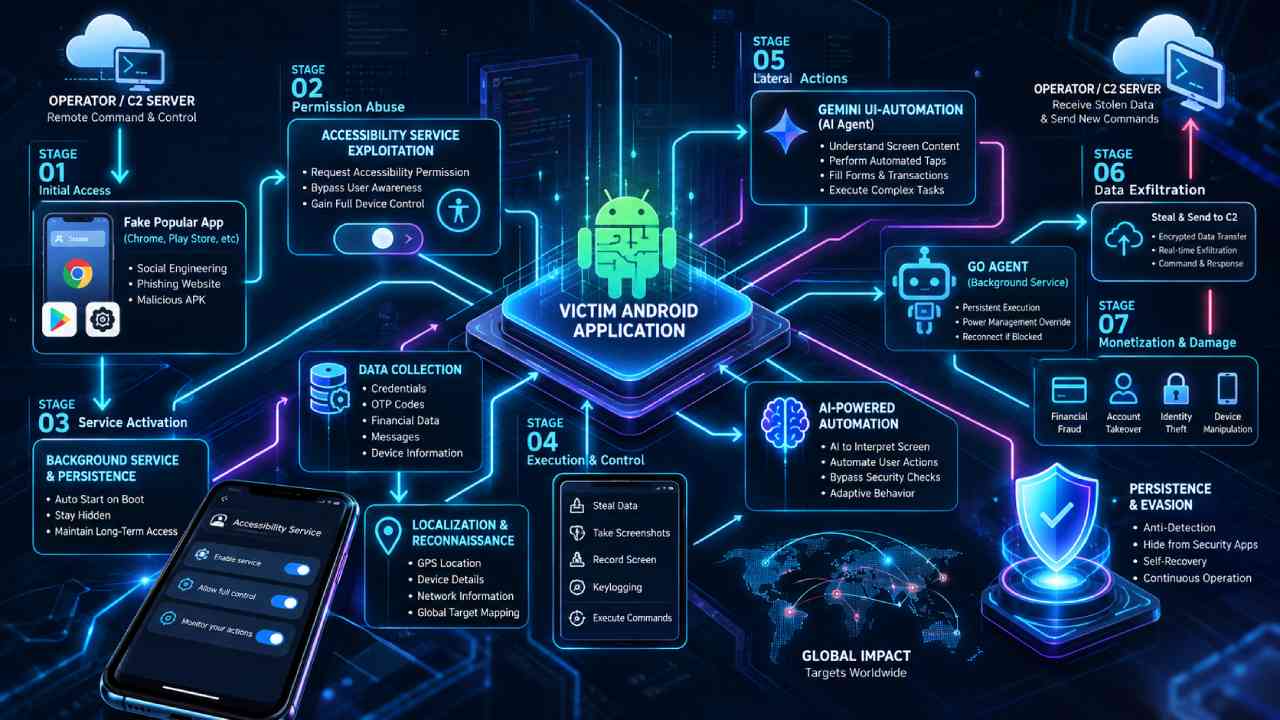
RatHat relies heavily on social engineering before its more advanced capabilities become useful. Researchers found that attackers can distribute it through targeted smishing and malicious advertising campaigns. Victims may then reach deceptive third-party download portals that encourage them to install an APK. Once installed, the malicious application can imitate familiar software. This strategy matters because many mobile attacks succeed before users notice anything unusual. Instead of displaying an obvious warning, the malware attempts to appear trustworthy. Moreover, users who install applications outside official stores may have fewer signals to help them judge authenticity. RatHat demonstrates why the first stage of mobile security often depends on cautious downloading habits. Advanced malware still needs an opportunity to enter the device.
Accessibility Features Become a Powerful Entry Point
Android’s Accessibility Service has legitimate purposes. It helps people interact with their devices when conventional controls are difficult to use. However, malicious applications can abuse the same capabilities when users grant unnecessary permissions. RatHat takes advantage of this opportunity. According to zLabs, it combines Accessibility abuse with local Android Debug Bridge pairing. The process can help the malware move beyond the normal Android application sandbox and establish components with shell-level privileges. As a result, the threat gains capabilities that an ordinary application should not have. This technique is especially concerning because it turns trusted system features into part of the attack chain. Therefore, users should treat unexpected accessibility requests with caution, particularly when the application’s main function does not require them.
Wireless Debugging Helps the Malware Reach Deeper
Wireless Debugging is useful for legitimate Android development and testing. RatHat, however, attempts to turn that feature into another step in its infection process. After gaining sufficient accessibility control, the malware can navigate toward developer settings and work through the pairing process. It can then establish local ADB access. This creates an important shift in the attack because shell-level access gives the malware greater freedom than a standard Android application. RatHat can also stage independent native components that support persistence. In practical terms, removing the original application may not always end every part of the infection. This layered approach makes the malware more challenging than a simple malicious APK. More importantly, it shows how attackers can connect several legitimate Android functions to build a much more powerful attack chain.
Artificial Intelligence Gives RatHat Greater Flexibility
The AI component is one of RatHat’s most distinctive features. According to Zimperium, the malware uses generative AI as part of its operational control. Researchers found techniques that allow it to interpret interface information and help determine actions on the device. This approach can make automated navigation more flexible when screen layouts change. Traditionally, malicious automation may depend heavily on fixed coordinates or predictable interface elements. However, AI can help software interpret what appears on a screen and react accordingly. That does not mean RatHat can magically control every Android device without limitations. Instead, AI adds another layer of adaptability to an already complex attack chain. In my view, this is the more important cybersecurity story. AI does not replace traditional malware techniques here. Rather, it strengthens methods that attackers already understand.
Banking Credentials and Authentication Codes Become Valuable Targets
Financial information sits near the center of RatHat’s objectives. Zimperium researchers found that the malware can display fake interfaces designed to resemble legitimate banking and payment applications. These overlays can trick victims into entering login information. In addition, RatHat can target one-time passwords and two-factor authentication codes. This combination is significant because stealing a password alone may not provide access when stronger authentication is active. Capturing both credentials and verification codes creates a more serious risk. The malware can also monitor information through Android accessibility mechanisms. Therefore, users may not immediately realize that sensitive data has been exposed. RatHat highlights why account security should not depend on a single defensive layer. Strong passwords remain important, but device security also matters when authentication information passes through the same compromised phone.
Persistence Makes RatHat Harder to Remove
Many users assume that deleting a suspicious application will solve a malware problem. RatHat challenges that assumption. Its infection process can establish native components outside the normal lifecycle of the original application. According to the zLabs analysis, these components can support persistence and may help restore parts of the infection. Researchers also documented techniques designed to interfere with removal attempts. Consequently, an infected device may require more careful remediation than simply pressing the uninstall button. This persistence strategy reveals an important trend in mobile malware development. Attackers increasingly want long-term access rather than a brief opportunity to steal information. For users who suspect a serious compromise, preserving important clean data and seeking reliable security guidance is safer than repeatedly interacting with an unknown malicious application.
Read Also: Website Design That Determines the Success of a Modern Online Platform
RatHat Reflects a Wider Shift in Mobile Cybercrime
RatHat is not appearing in isolation. Mobile devices have become increasingly valuable targets because they contain personal conversations, financial applications, authentication tools, and work accounts. Zimperium’s broader 2026 research describes attackers using AI across mobile attack workflows, including social engineering and malware operations. RatHat provides a concrete example of this direction. It combines phishing-style distribution, application impersonation, permission abuse, ADB access, persistence, and AI-assisted control. Therefore, the malware is notable not because every individual technique is new. Its strength comes from combining several methods into one coordinated infection chain. As smartphones become central to digital identity, attackers have stronger incentives to pursue control at the device level. Mobile security should consequently receive the same attention that users already give to desktop computers.
Safer Downloading Habits Can Reduce Exposure
Complex malware does not make basic security habits irrelevant. In fact, RatHat shows why those habits still matter. Users should avoid installing APK files from unfamiliar links, unexpected text messages, advertisements, or imitation download pages. Instead, applications should come from trusted sources whenever possible. Users should also examine permission requests carefully. A simple application that suddenly asks for Accessibility Service access deserves additional scrutiny. Likewise, unexpected instructions involving developer settings or Wireless Debugging should raise concern. Keeping Android and installed applications updated can also reduce exposure to known security weaknesses. Furthermore, users should review unfamiliar applications rather than ignoring them. No single precaution can eliminate every mobile threat. However, several small security decisions can make it harder for malware to establish the access it needs.
RatHat Shows Why Android Security Is Becoming More Complex
RatHat offers a glimpse of how mobile malware may continue to evolve. Its most important feature is not AI alone. Instead, the threat combines AI with social engineering, trusted Android functions, persistence mechanisms, and financial targeting. This combination creates a more adaptable attack model. At the same time, the infection still depends on opportunities created during the earlier stages of the attack. That gives users an important defensive advantage. Careful app installation, limited permissions, trusted download sources, and attention to unusual system requests remain valuable. Meanwhile, security researchers and platform developers face a different challenge. They must prepare for malware that can interpret interfaces and automate actions more dynamically. RatHat may represent one malware family, but the techniques behind it point toward a broader change in the mobile security landscape.